Enforce MFA Across Your Entire Organization with One Setting
Your organization has an MFA policy. It says every user must enable multi-factor authentication. It has been in the handbook for years. And right now, there are almost certainly users in your systems who have never finished MFA setup — and they are logging in without difficulty.
That is not a policy problem. It is an enforcement problem.
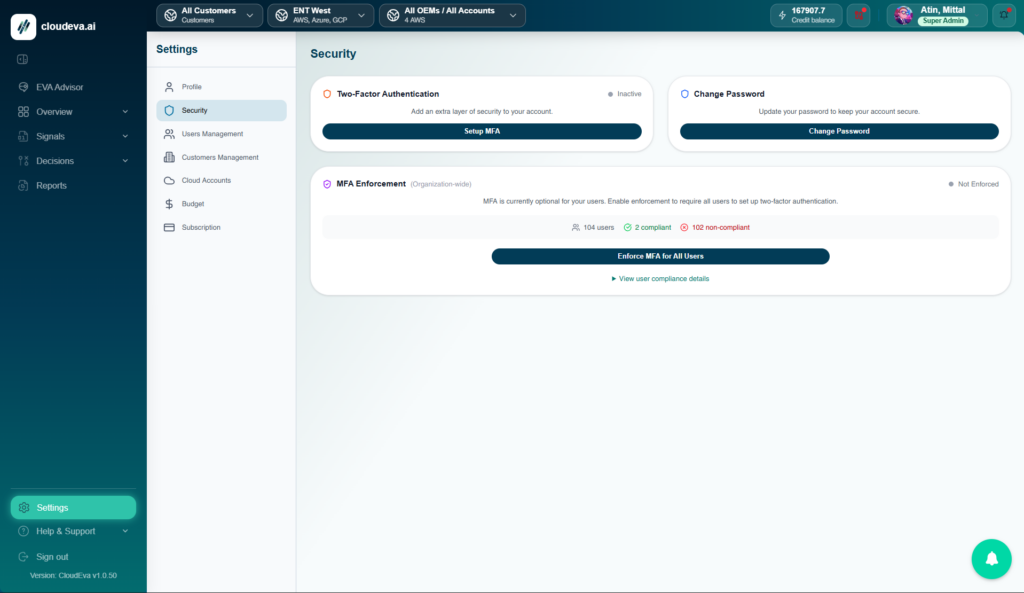
Cloudeva closes it with a single setting. Super Admins can require MFA across the entire organization, and any user who has not completed setup is stopped at login until they do. No grace period, no reminder campaign, no helpdesk queue. The feature is available on every Cloudeva plan.
The wider case for MFA as a security baseline is covered in our post on why multi-factor authentication is the non-negotiable cloud security baseline. This page is about the mechanism — what enforcement actually does, what users experience, and how you prove it to an auditor.
MFA Policy Is Not MFA Enforcement
An MFA policy is a document. It describes what should happen. Enforcement is a system setting. It determines what does happen, regardless of whether a user remembers, agrees, or is having a busy week.
Most platforms let you enable MFA as an option. They send reminders, show a prompt at login, and allow a grace period in which users dismiss it and carry on. When the grace period ends, the system sends another reminder. Then another.
What is left behind is a set of accounts that never completed setup. They tend to be the same accounts that reuse passwords and ignore security prompts — which makes them the ones most worth attacking. That residue is not a communications problem. It is an enforcement gap, and it is the gap attackers look for. A policy without a mechanism behind it is a liability, not a control.
How Cloudeva Forces MFA Setup Organization-Wide
A Super Admin turns on organization-wide MFA enforcement from a single setting in the Cloudeva admin panel. Once it is on:
- Any user who has not completed MFA setup is stopped at login.
- They are not shown a reminder, a countdown, or a “set up later” option.
- They are walked through setup on the spot, at the point of access.
- Once setup is complete, they continue into the platform as normal.
- They cannot switch MFA off from their side afterwards.
There is no grace period and no user-side bypass. The only exceptions are ones an admin grants deliberately, and each one is recorded — covered further down.
What Users See at Login
This is the flow for a user who has not yet completed MFA setup when enforcement is switched on.
1. The user signs in as normal
They enter their credentials. Cloudeva validates the password.
2. They are stopped at the MFA gate
Instead of the dashboard, they see a mandatory MFA setup screen. No dismiss button, no “remind me later.” The only way forward is completing setup.
3. They complete guided setup
They scan the QR code with an authenticator app — Google Authenticator, Authy, 1Password, Microsoft Authenticator, Duo — enter the verification code, and confirm.
4. Access is granted
They continue into the platform. Every subsequent login requires the authenticator code, and MFA cannot be turned off from the user side.
For IT teams: No IT involvement is required in this flow. Users enrol themselves, in real time, at the point of access. No tickets, no chasing emails, no manual tracking of who has finished.
Screenshot needed: The blocked-login / mandatory setup screen a user actually sees. Second most valuable asset on the page.
See MFA Compliance at a Glance
Enforcement is half the job. For a security review or an audit you also need proof. Cloudeva gives Super Admins a compliance dashboard showing MFA status for every user in the organization:
- Users with MFA setup completed, and users still pending
- Per-user MFA status
- Admin-granted exemptions, and who granted them
- An exportable record for internal security reviews and audit evidence
When someone asks whether every user has completed MFA setup, the answer comes from one screen rather than a manual account-by-account census.
Exemptions and Account Recovery
Two questions come up in every security review, so they are worth answering directly.
Can anyone be exempted? Yes, but only by an admin, deliberately, for a named user — and the exemption appears in the compliance dashboard. That matters more than a blanket claim of zero exceptions. Real organizations occasionally need a service account or a break-glass path; what separates a control from a loophole is whether the exception is visible.
What if a user loses their phone? A Super Admin can reset MFA for that user, which returns them to the setup flow at their next login so they can enrol a new device. The reset is recorded, so recovery does not leave an unexplained gap in your audit trail.
Works with the Authenticator App Your Team Already Has
Cloudeva’s MFA enforcement works with TOTP-based authenticator apps, so users do not need to install anything specific. Supported apps include Google Authenticator, Authy, 1Password, Microsoft Authenticator and Duo, along with other TOTP-compliant applications.
Setup stays familiar for users while administrators keep centralized control over enforcement.
Available on Every Plan
MFA enforcement is not held behind an Enterprise tier. Every Cloudeva customer, at any plan level, gets the same enforcement capability and the same compliance dashboard. Security controls that only larger customers can afford are not really a baseline.
Frequently Asked Questions
Q1. How do I enforce MFA for all users in my organization?
A Super Admin turns on organization-wide MFA enforcement from a single setting in the Cloudeva admin panel. From that point, any user who has not completed MFA setup is stopped at their next login and guided through setup before they can continue. No further admin action is needed.
Q2. What is the difference between enabling MFA and enforcing MFA?
Enabling MFA makes it available as an option, so each user decides whether to complete setup. Enforcing MFA removes that choice. In Cloudeva’s enforcement mode, a user cannot reach the platform without completing MFA setup, and cannot switch MFA off afterwards.
Q3. Can a user skip or bypass MFA once enforcement is turned on?
No. There is no user-side bypass, no grace period, and no “remind me later” option. The only route to the platform is completing MFA setup. Exemptions can only be granted by an admin, and every exemption is recorded in the compliance dashboard.
Q4. What happens to a user who has not set up MFA when enforcement is turned on?
At their next login they are taken straight to the MFA setup screen. They scan a QR code with an authenticator app, enter the verification code, and continue into the platform. There is no option to defer.
Q5. What happens if a user loses the device with their authenticator app?
A Super Admin can reset MFA for that individual user from the admin panel, which returns them to the setup flow at their next login so they can enrol a new device. The reset is recorded in the compliance dashboard, so recovery does not create an unlogged gap in your audit trail.
Q6. How do administrators check MFA compliance across the organization?
The compliance dashboard shows MFA status for every user in one view, including who has completed setup, who is still pending, and who holds an admin-granted exemption. It removes the need to check accounts individually or maintain a spreadsheet.
Q7. Does Cloudeva MFA work with Google Authenticator and Authy?
Yes. Cloudeva supports TOTP-based authenticator apps, including Google Authenticator, Authy, 1Password, Microsoft Authenticator and Duo. Users do not need to install a specific app, and the enforcement feature is available on all Cloudeva plans.
Ready to make MFA a requirement rather than a request? Start your free trial at cloudeva.ai, or talk to us about enforcement across your organization.