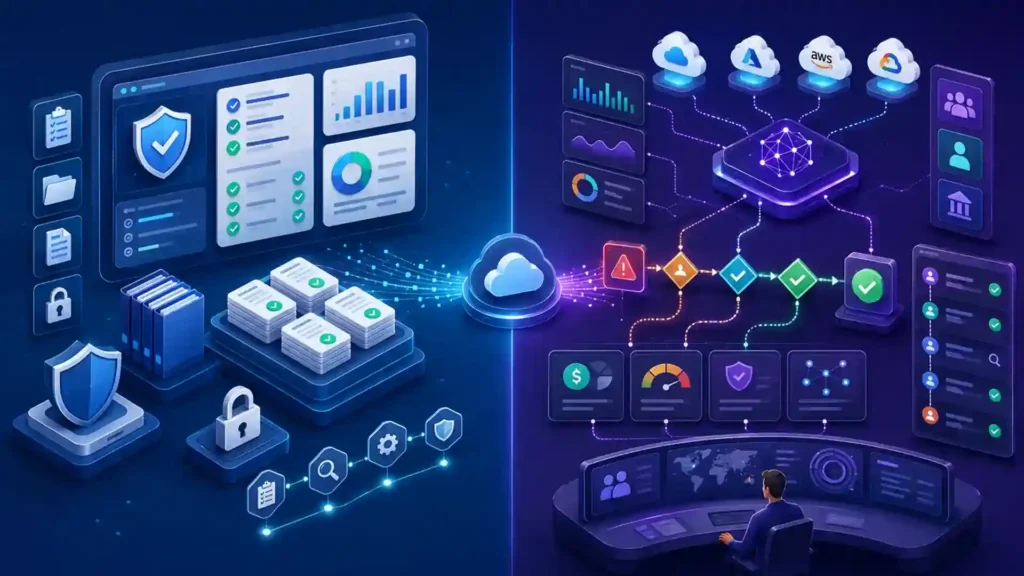
Drata is a continuous compliance platform. Cloudeva.ai is a cloud decision intelligence system. Understanding cloud governance vs compliance is the clearest way to see what each governs and where the gap matters.
The Cloud Governance vs Compliance Distinction That Actually Matters
Drata has built a strong reputation in continuous compliance automation maintaining real-time evidence of security controls for SOC 2, GDPR, HIPAA, and other frameworks. For security and compliance teams, it delivers genuine value by removing the scramble that used to precede every audit.
Cloudeva.ai operates in a different domain: continuous cloud governance. In the cloud governance vs compliance debate, this is the distinction that changes what your team actually does with what they find not just conformance to controls, but confident, documented decision-making across the infrastructure lifecycle. Both are “continuous.” The difference is what they’re continuously monitoring and what they enable your team to do with what they find.
What Drata Gets Right
Drata’s continuous monitoring model is well-designed for compliance-heavy organizations. It integrates with cloud providers, identity platforms, code repositories, and HR systems to maintain a real-time view of control adherence. When a control lapses, Drata surfaces it and guides remediation.
Its audit-ready reporting has made the annual SOC 2 audit significantly less painful for the engineering and security teams that used to spend weeks assembling evidence manually. For organizations where compliance certification is a business requirement, Drata removes substantial operational burden.
The Governance Gap Drata Doesn’t Address
Drata’s framework is compliance-centric: the controls are defined externally by a standard (SOC 2, ISO 27001, etc.), and Drata monitors whether your environment meets them. The governance question it answers is: are we compliant? That is the compliance side of the cloud governance vs compliance equation.
Cloud governance requires a broader question: are we making the right decisions about our cloud infrastructure at the cost level, the risk level, and the operational level and can we demonstrate that we are?
Drata does not surface cost signals. It does not advise on infrastructure decisions. It does not record the reasoning behind provisioning choices, scaling decisions, or governance exceptions. Those are cloud governance concerns, and they fall outside Drata’s scope by design.
The EVA Loop in Practice
When a cloud cost or risk signal surfaces in Cloudeva.ai, it moves through the EVA loop: Explain, Verify, Advise.
Explain: Cloudeva.ai surfaces the context what service generated the signal, which environment, what the baseline looks like, what infrastructure activity if any corresponds to the timing.
Verify: The signal is cross-referenced with known patterns and team context. Is this expected? Is it anomalous? Is it a known exception with a prior governance decision attached?
Advise: A structured recommendation is surfaced not a rule violation notification, but an advisory with evidence. Your team can evaluate it, act on it, or override it with documented rationale. monitoring and it is the operational expression of the cloud governance vs compliance divide. One governs conformance. The other governs decision quality.
Decision Records vs Compliance Evidence
Drata produces compliance evidence: time-stamped records showing that controls existed and were operating. This satisfies auditors.
Cloudeva.ai produces decision records: time-stamped records showing that when a signal surfaced, someone evaluated it, a recommendation was made, and a decision was taken. This satisfies both auditors and leadership because it demonstrates that cloud governance is an active practice, not just a passive monitoring exercise.
For boards and executive teams reviewing cloud governance posture, the decision record is as important as the compliance evidence. It shows judgment, not just conformance.
Cost Signals: The Category Drata Doesn’t Touch
Cloud cost governance is entirely outside Drata’s scope which is the most tangible example of what cloud governance vs compliance means in practice. Drata does not surface cost anomalies, does not advise on spending decisions, and does not maintain a record of financial governance decisions made at the infrastructure level.
Cloudeva.ai’s cost signal layer fills this gap directly. When spend patterns shift whether due to scaling, misconfiguration, team behavior, or pricing changes Cloudeva.ai surfaces the signal with context and guides the team to a confident decision.
For FinOps leaders who need governance coverage across both cost and compliance domains, the combination of Drata (compliance) and Cloudeva.ai (decision intelligence) provides more complete coverage than either alone.
The Regulated Industry Context
In BFSI, healthcare, and other regulated industries, cloud governance requirements are expanding beyond security controls to include financial controls and operational decision documentation. Frameworks like DORA explicitly require documented decision processes for cloud operational resilience.
Cloudeva.ai’s persistent decision intelligence model where every significant cloud signal is processed through EVA and every decision is recorded is designed to meet this emerging standard. It complements Drata’s compliance automation by covering the governance layer that compliance frameworks do not define.
The Bottom Line
Drata and Cloudeva.ai are not alternatives to each other. They govern different layers of the same cloud environment. Drata keeps your compliance posture current. Cloudeva.ai keeps your decision-making sharp.
Organizations that treat these as comparable products without understanding cloud governance vs compliance as distinct disciplines will end up with a gap: either in compliance evidence or in decision governance. Organizations that deploy both have a more complete picture.
Sharp. Smart. Certain.
If you’re evaluating cloud governance tools more broadly, see how Cloudeva.ai compares to Vanta, Drata, Flexera, and Spot.io.
See how Cloudeva.ai handles cloud governance in a live environment book a 20-minute demo.
See How Cloudeva.ai Compares
Explore the full competitive landscape – how Cloudeva.ai positions against every major cloud cost and governance tool in the market.
→ cloudeva.ai/our-model/competition/
Cloudeva.ai – Sharp. Smart. Certain.
Frequently Asked Questions
What is cloud governance?
Cloud governance establishes policies, controls, and best practices for managing cloud resources securely and efficiently.
How is cloud governance different from compliance automation?
Cloud governance focuses on managing cloud operations, while compliance automation helps organizations meet regulatory requirements through automated checks and reporting.
Why compare Cloudeva.ai and Drata?
The comparison helps organizations understand whether they need broader cloud governance capabilities or primarily compliance automation.
Who should use cloud governance platforms?
Cloud governance platforms are useful for organizations managing multi-cloud environments, controlling costs, improving security, and maintaining operational consistency.
Frequently Asked Questions
What is the difference between Cloudeva.ai and Drata?+
Drata automates compliance: it collects evidence and monitors controls so audits like SOC 2 and ISO 27001 run continuously. Cloudeva.ai governs decisions: every cloud change is explained, verified, and reviewed by an owner. Compliance proves you met a standard; governance decides what should happen in the first place.
Does Cloudeva.ai replace Drata?+
No. If you need audit certification, a compliance automation platform remains the right tool for evidence collection. Cloudeva.ai addresses the layer above it — the day-to-day cloud decisions that determine whether your environment stays worthy of the certificate between audits.
Can compliance automation and decision governance work together?+
They're complementary. Decision records from Cloudeva.ai give compliance teams the "why" behind every change, which strengthens audit narratives; compliance requirements in turn become policies EVA verifies changes against. Together they close the gap between passing audits and actually being governed.